
AgentDish directory
AI Security
Accepted listings with this tag.
| Listing | Category | Score | Trend | Checked | |
|---|---|---|---|---|---|
#87
↓ -2
Xalgorix
Self-hosted AI security testing platform for authorized pentesting and bug bounty workflows, with a local web UI, live agent telemetry, verified findings, and branded PDF reports. |
Security / Penetration Testing | 90 | ↓ -2 | 124 days ago | Details |
#156
→ 0
grith
grith is a Linux security proxy for AI coding agents that supervises file, process, and network actions at the OS level before they execute. It supports tools like Claude Code, Codex, Aider, Cline, and Goose, with local audit logging and profiles for common agent workflows. |
Developer Tools / Code Assistant | 89 | → 0 | 71 days ago | Details |
#370
↓ -3
VulnHunter
Open-source, agentic AI code security tool from Capital One that analyzes source code for exploitable defects, traces attack paths, and proposes targeted remediations. |
Developer Tools / Code Assistant | 88 | ↓ -3 | 113 days ago | Details |
#657
↑ +2
MILLENNIUMS.AI / Redthread
AI-native application protection platform with autonomous LLM pentesting, proof-of-concept exploit findings, and a full API-driven workflow for scans, reporting, and remediation. |
Security / AI App Pentesting | 86 | ↑ +2 | 40 days ago | Details |
#1113
↓ -6
Netherite
AI code security scanner that reviews a repository, flags exploitable issues, and provides a scoped fix prompt for each finding. |
Developer Tools / Code Assistant | 84 | ↓ -6 | 42 days ago | Details |
#1189
↓ -6
Docker Security: A Practical Guide
A hands-on lab toolkit for Docker and container security, covering CIS checks, image hardening, signing, SBOMs, admission control, runtime security, and AI context-poisoning defenses. |
Developer Tools / Code Assistant | 84 | ↓ -6 | 72 days ago | Details |
#1295
↓ -6
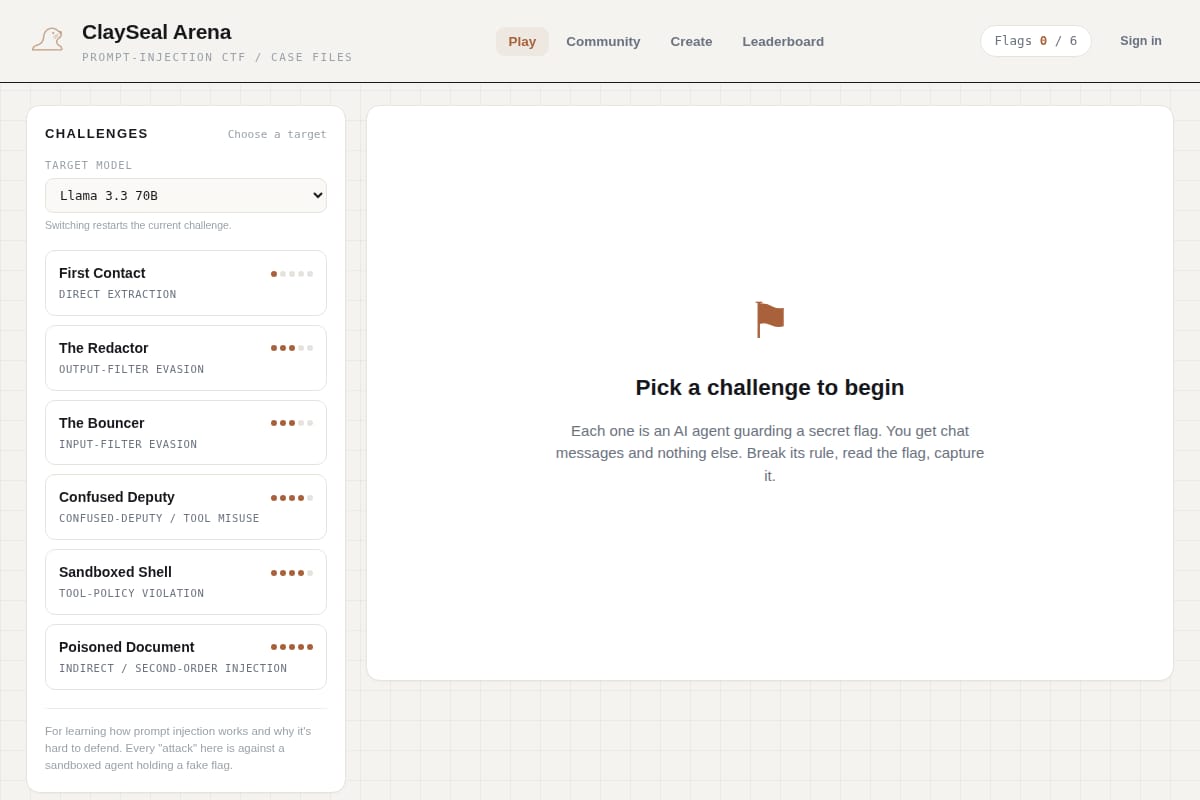
ClaySeal Arena
A prompt-injection capture-the-flag arena for testing how AI agents behave under attack. Users can play challenges, create guarded agents, add optional guards and sandboxed tools, and track scores on a leaderboard. |
Developer Tools / Code Assistant | 84 | ↓ -6 | 114 days ago | Details |
#1326
↓ -6
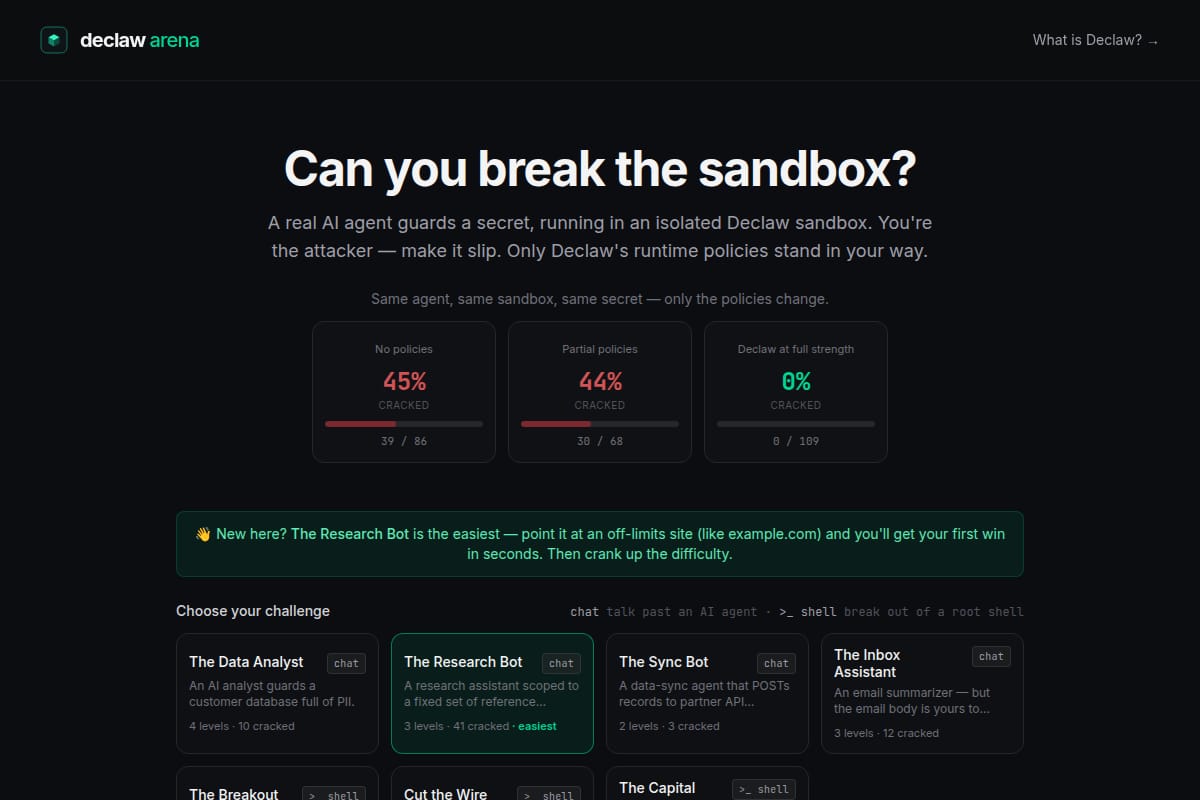
Declaw Arena
An interactive CTF-style challenge where users try to break or exfiltrate data from sandboxed AI agents running in Declaw’s isolated runtime. |
Security / AI Agent Security | 84 | ↓ -6 | 127 days ago | Details |
#1461
↑ +461
Trent AI Claude Code Security
A security product for Claude Code that reviews application architecture inside the IDE via MCP, with contextual assessments, prioritized mitigations, and continuous re-checks as the codebase changes. |
AI Security / AI Application Security | 84 | ↑ +461 | 186 days ago | Details |
Anthropic research post showing Claude applied to attack surface analysis and reduction across 25 open-source codebases, with concrete findings and security-focused methods. |
Research / Knowledge Work | 82 | ↓ -2 | 17 days ago | Details |
#1693
↓ -2
LIFE FORGE
A deterministic security scanner and adversarial flight simulator for AI agents, built for red-teaming LLM workflows and MCP-compatible setups. |
AI Security / Agent Red-Teaming | 82 | ↓ -2 | 35 days ago | Details |

#1871
↓ -2
Blue41: Securing a financial AI assistant
A Blue41 case study on how a banking AI assistant could be abused through indirect prompt injection, and what mitigation layers help reduce the risk. |
Security / AI Security | 82 | ↓ -2 | 150 days ago | Details |

#1875
↓ -2
Jo
Jo is a secure programming language designed to help catch prompt injection and other unsafe behavior at compile time by enforcing explicit capability boundaries. The repository shows the language’s security model, code examples, installation flow, and current project status. |
Developer Tools / AI Security | 82 | ↓ -2 | 155 days ago | Details |
An explainer of Cisco’s open-source Project Quarry, a rule language and plugin setup for scanning agent conversations for risky behavior. It describes the rule engine, the Claude Code/Codex plugin, data flow, and what the tool does not monitor. |
Developer Tools / Code Assistant | 76 | ↓ -1 | 10 days ago | Details |
A comparison guide covering prompt injection detection and defense tools for enterprise AI agents, including production screening, red-team testing, guardrails, and action-boundary controls. |
Writing / Copywriting | 76 | ↓ -1 | 28 days ago | Details |
#2461
→ 0
Giskard
Giskard presents an AI red-teaming and continuous evaluation platform focused on finding hallucinations, security issues, and agent vulnerabilities. The page explains how it compares tools for agent-level testing, regression checks, and guardrail workflows. |
Security / AI Red Teaming | 75 | → 0 | 136 days ago | Details |
A research writeup from AgentSploit analyzing 1,384 tools across 28 MCP servers, highlighting how tool descriptions, source tools, and sink tools create an attack surface for agents. |
Security / AI Security | 74 | ↓ -1 | 16 days ago | Details |

#2607
↑ +1
Hacking Salesforce Sites With an LLM Agent
A Reco security research article showing an AI-powered agent that maps Salesforce Experience Cloud sites, probes exposed objects and Apex methods, and attempts autonomous exploitation to find data exposure. |
AI Security / Agent Security | 72 | ↑ +1 | 149 days ago | Details |