
AgentDish directory
security
Accepted listings with this tag.
| Listing | Category | Score | Trend | Checked | |
|---|---|---|---|---|---|
#1227
↓ -6
Kotro
Kotro is a local control plane for coding agents that governs MCP tool actions and LLM traffic with one binary. The page shows install options, supported clients, dashboard access, and concrete controls like schema pinning, redaction, cache, budget, and circuit breaker behavior. |
Developer Tools / Code Assistant | 84 | ↓ -6 | 94 days ago | Details |
#1233
↓ -6
Clawx
An open-source agent-driven package manager for versioned, checksummed, approval-gated tasks run through Claude Code, Codex, Gemini CLI, OpenCode, or Antigravity. |
Developer Tools / AI Agent Infrastructure | 84 | ↓ -6 | 95 days ago | Details |
#1250
↓ -6
Hotcell
Hotcell is a self-hostable sandbox SDK for AI agents that runs isolated sandboxes on local hardware or servers. The page shows setup, CLI commands, key handling, egress control, and support for containers or microVMs. |
Developer Tools / AI Developer Tooling | 84 | ↓ -6 | 102 days ago | Details |
#1288
↓ -6
B.I.O.M.A. Framework
A local Rust-plus-Python middleware layer for LLM apps that claims to reduce token usage and add in-process security checks before prompts are sent to a provider. |
Developer Tool / LLM middleware | 84 | ↓ -6 | 113 days ago | Details |
#1365
↓ -6
agent-vault-proxy
A loopback HTTPS proxy that swaps placeholders for real API keys at request time, keeping secrets out of the agent process. It uses Bitwarden Secrets Manager and supports scoped bindings for hosts, methods, and paths. |
Developer Tool / Security | 84 | ↓ -6 | 148 days ago | Details |
#1373
↓ -6
AgentTrust ID
Runtime authorization platform for AI agents with open-source SDKs in Python, TypeScript, Go, Java, and Rust. The page says the hosted service is in production, supports per-action checks, scoped delegation, revocable tokens, and a shared authorization model across MCP tools, agent-to-agent calls, and direct API integr |
AI Developer Tool / Agent Security / Authorization | 84 | ↓ -6 | 152 days ago | Details |
#1375
↓ -6
Sandfence
A minimal native macOS sandbox for running Claude Code or Codex with OS-enforced limits on what the agent can touch. |
Developer Tools / Security | 84 | ↓ -6 | 154 days ago | Details |
#1379
↓ -6
Defending Code Reference Harness
An open-source reference implementation for autonomous vulnerability discovery and remediation with Claude. It includes Claude Code skills for threat modeling, scanning, triage, patching, plus a harness for running a recon → find → verify → report → patch pipeline. |
Security / AI Security | 84 | ↓ -6 | 155 days ago | Details |
#1391
↓ -6
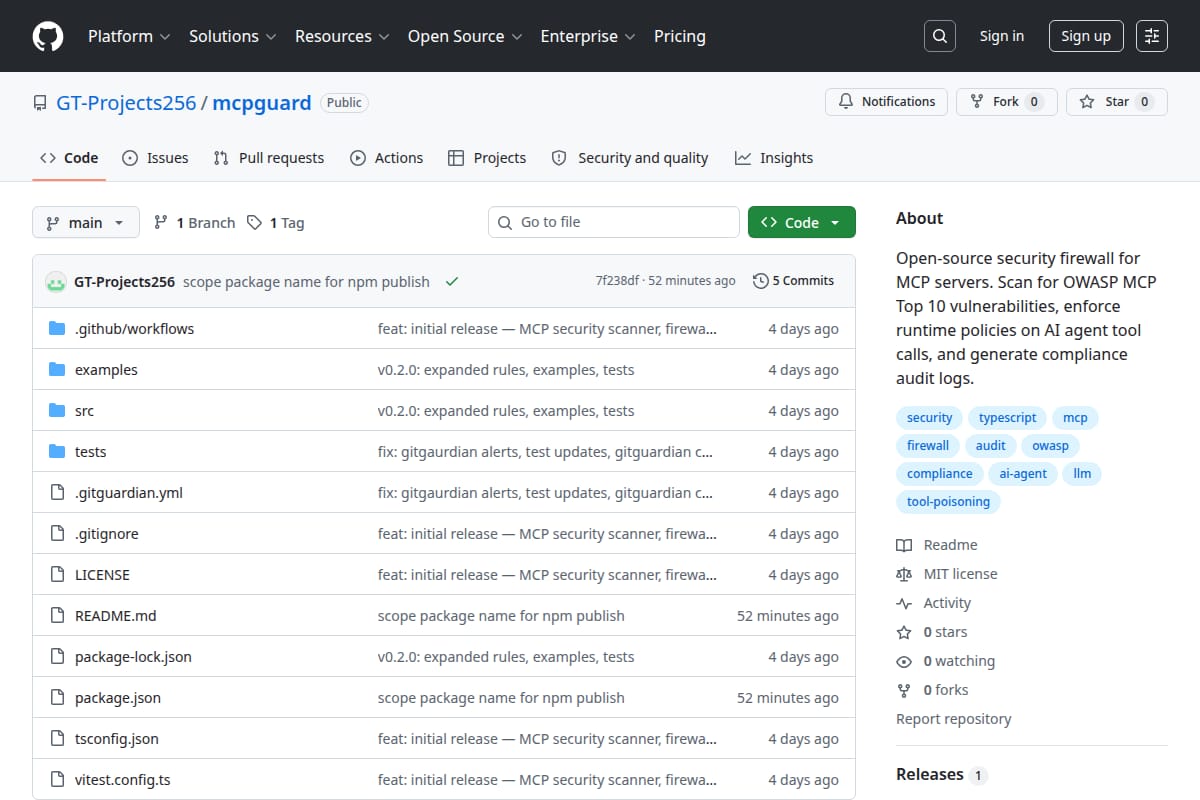
mcpguard
Open-source security scanner and firewall for MCP servers. It scans configs for common MCP risks, enforces runtime policies on tool calls, and produces audit logs, with CLI commands, policy examples, and a programmatic API. |
Developer Tools / Security | 84 | ↓ -6 | 160 days ago | Details |
#1403
↓ -6
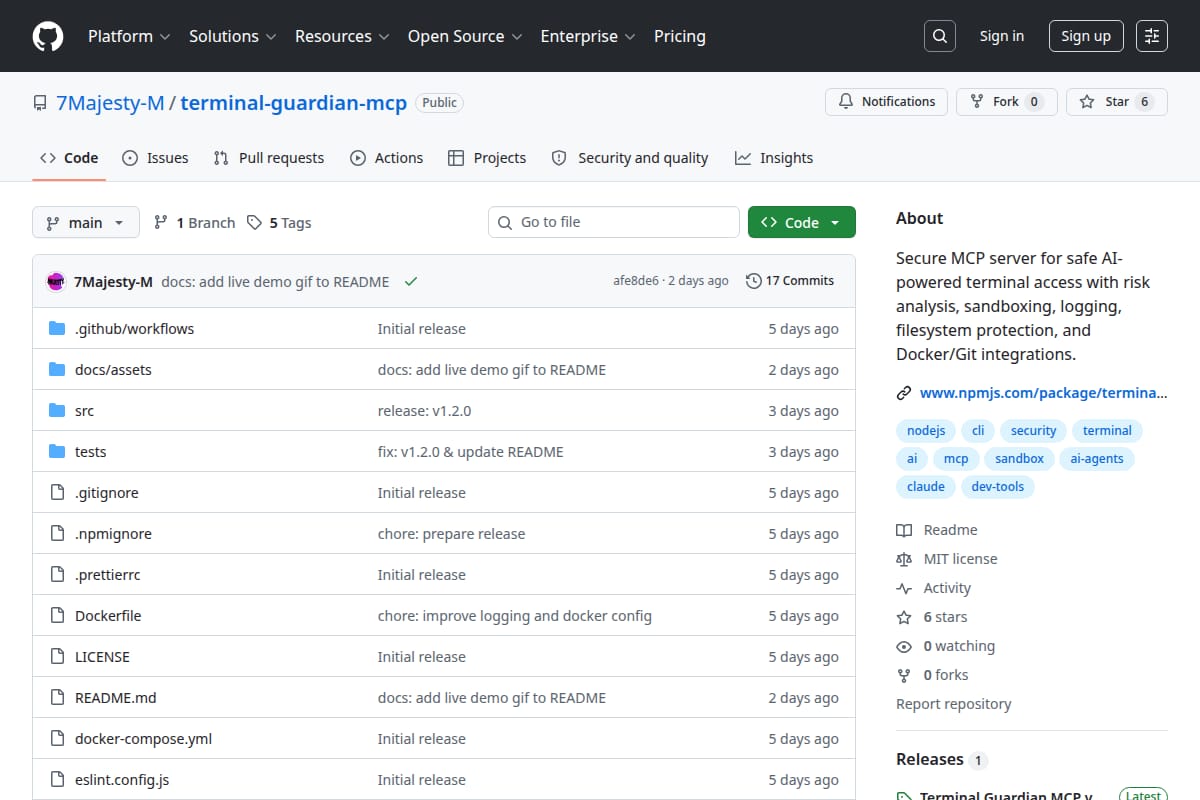
terminal-guardian-mcp
A secure Model Context Protocol server that gives AI assistants controlled terminal access with risk analysis, sandboxing, logging, filesystem protection, and optional Docker and Git features. |
Developer Tools / MCP Servers | 84 | ↓ -6 | 168 days ago | Details |
#1422
↓ -6
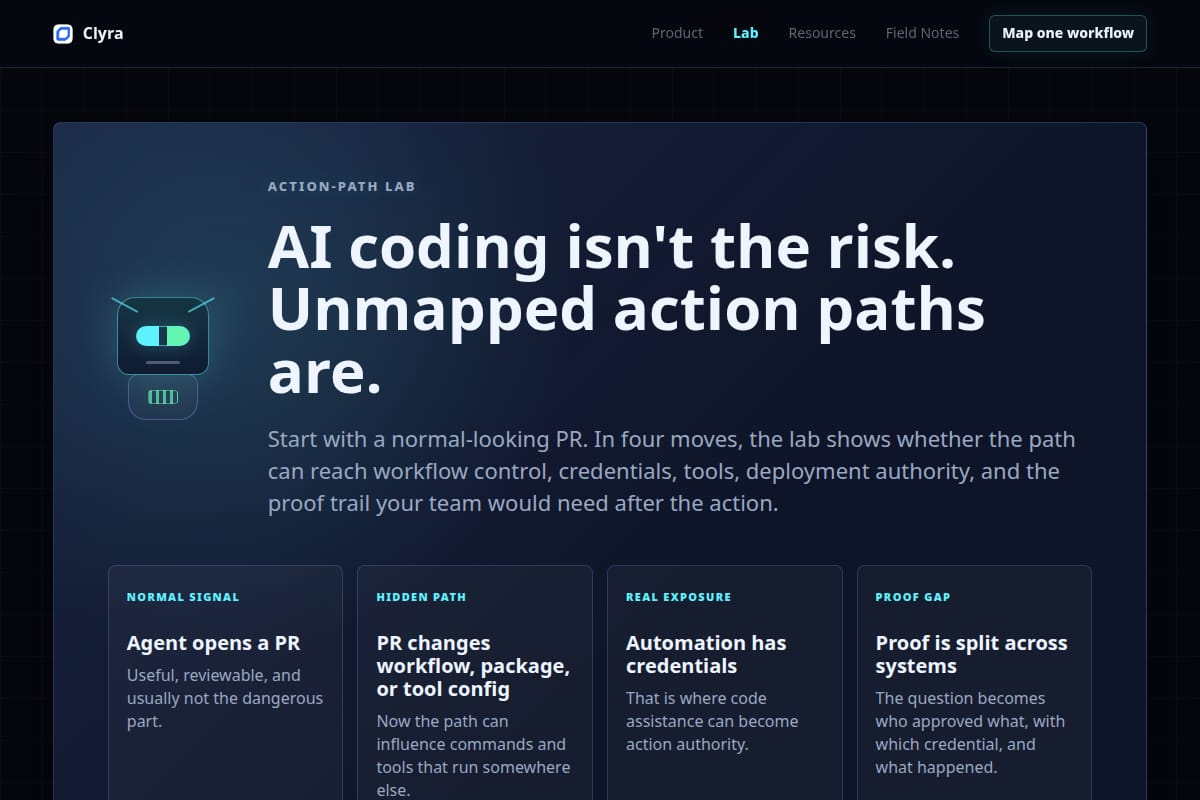
AI Action Path Lab
An interactive lab for tracing how AI-assisted engineering workflows can reach repos, CI/CD, credentials, tools, approvals, and proof trails. |
Productivity / Workflow Automation | 84 | ↓ -6 | 177 days ago | Details |
#1446
↑ +208
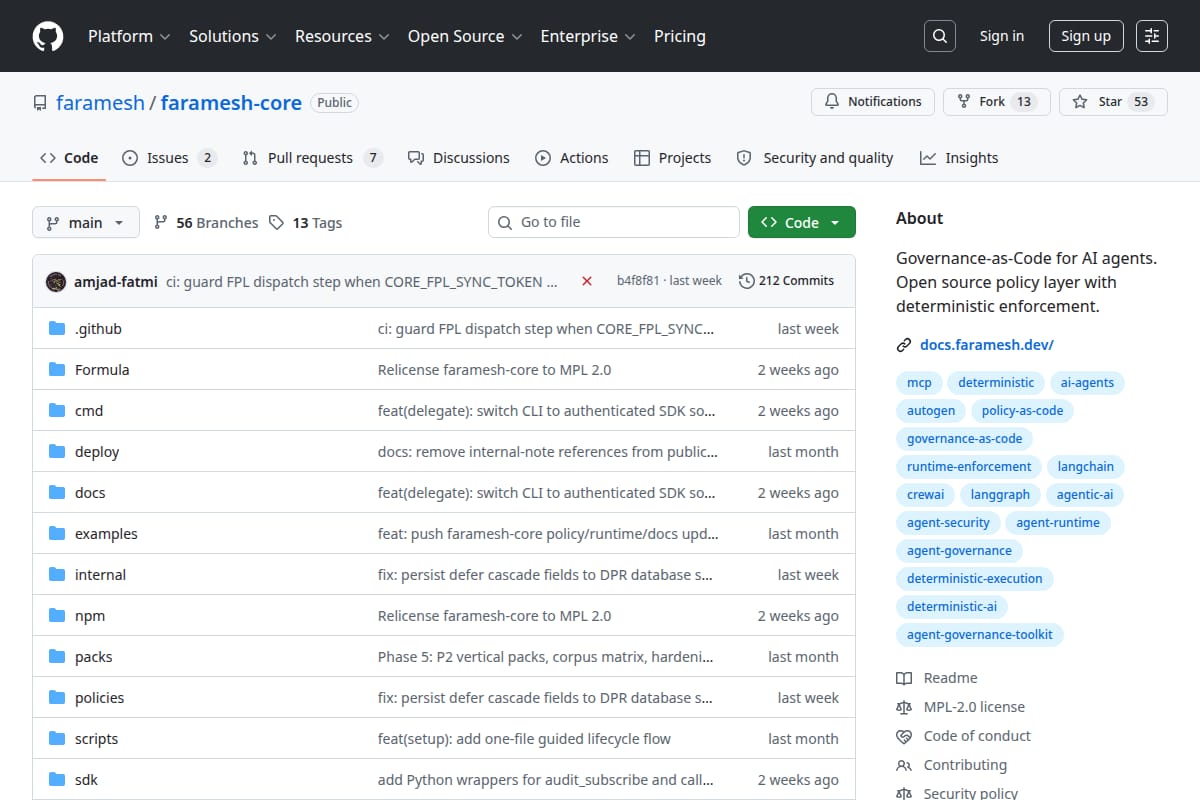
Faramesh
Runtime governance and containment for AI agents. Faramesh sits between an agent and its tools to enforce policy checks, approval steps, credential isolation, and tamper-evident audit logs before risky actions execute. |
Developer Tools / AI Governance / Agent Security | 84 | ↑ +208 | 185 days ago | Details |
#1461
↑ +461
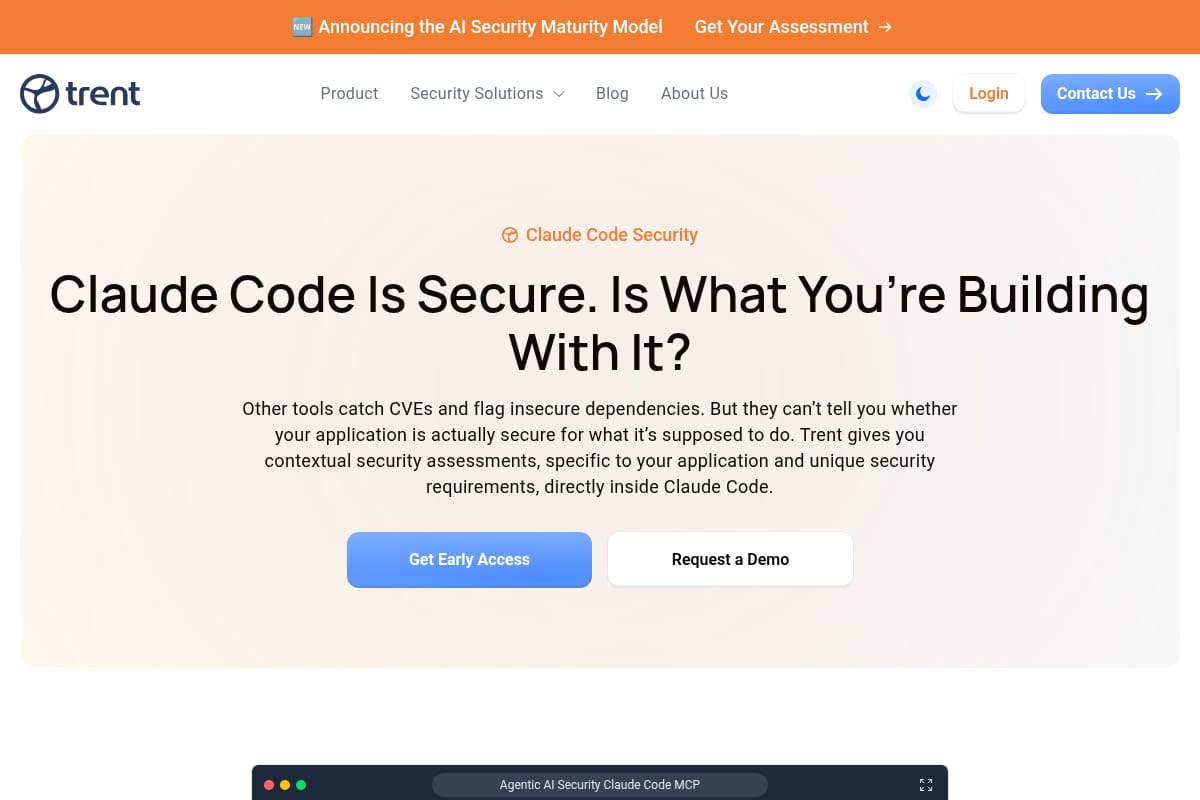
Trent AI Claude Code Security
A security product for Claude Code that reviews application architecture inside the IDE via MCP, with contextual assessments, prioritized mitigations, and continuous re-checks as the codebase changes. |
AI Security / AI Application Security | 84 | ↑ +461 | 186 days ago | Details |
#1467
↓ -3
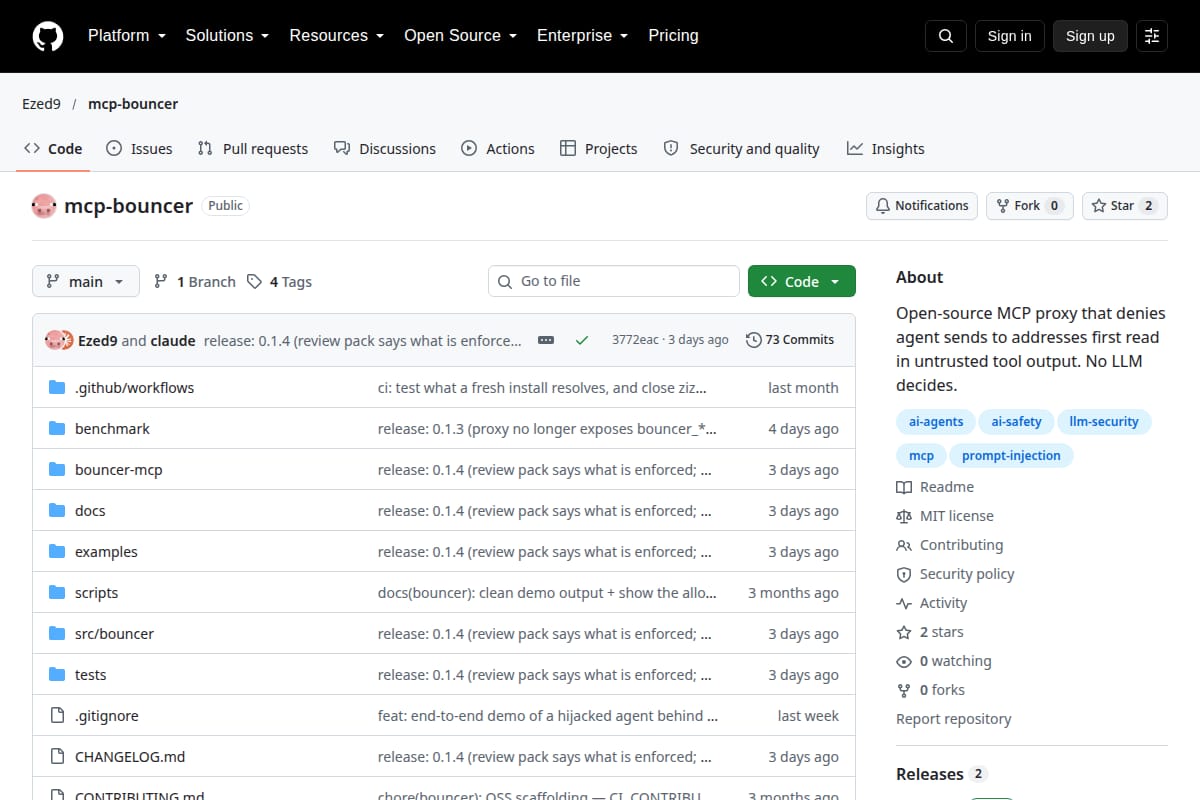
mcp-bouncer
Open-source MCP proxy that blocks agent send/share actions when the destination first appears in untrusted tool output. It uses deterministic rules rather than an LLM and logs every allow/deny decision. |
Developer Tools / AI Safety / MCP Security | 83 | ↓ -3 | 11 days ago | Details |
#1473
↓ -3
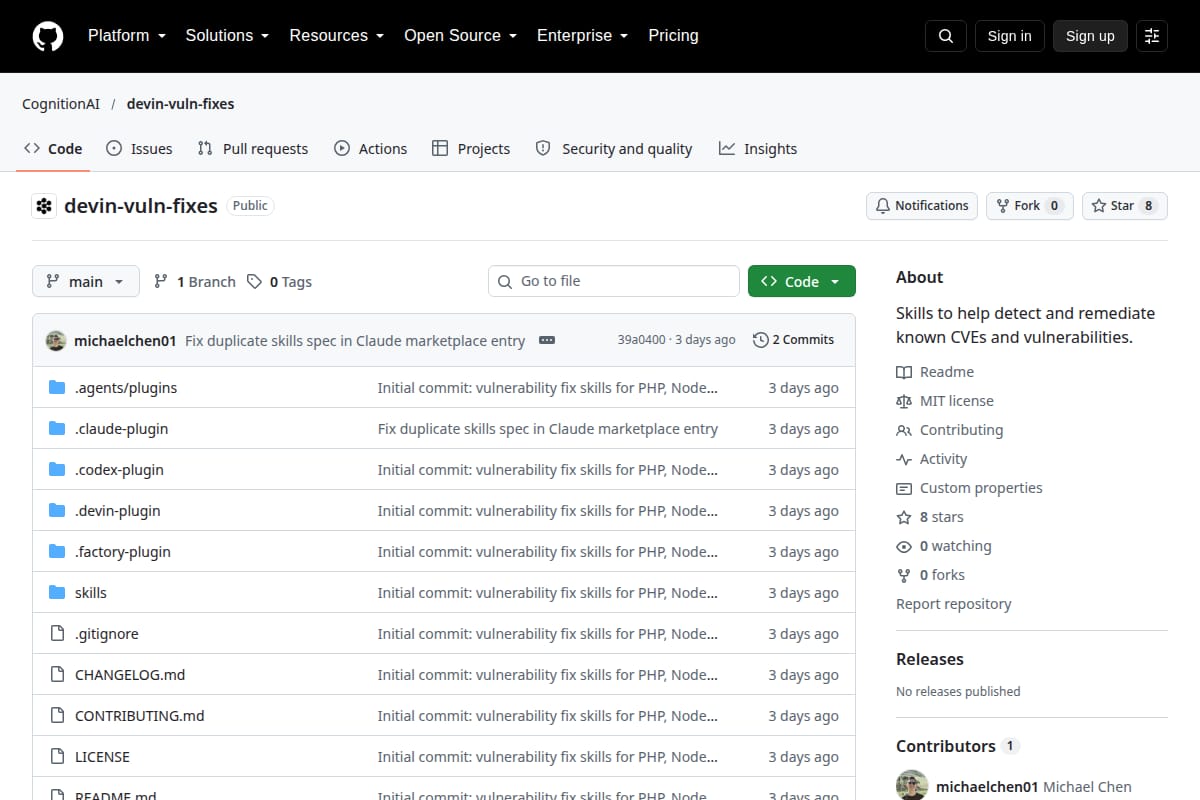
Devin vulnerability-fixing skills
Repository of agent skills for detecting and patching known CVEs in PHP, Node.js, and GitLab environments, with installation instructions and support across multiple coding agents. |
Developer Tool / AI Coding Agent Skill | 83 | ↓ -3 | 13 days ago | Details |
#1481
↓ -3
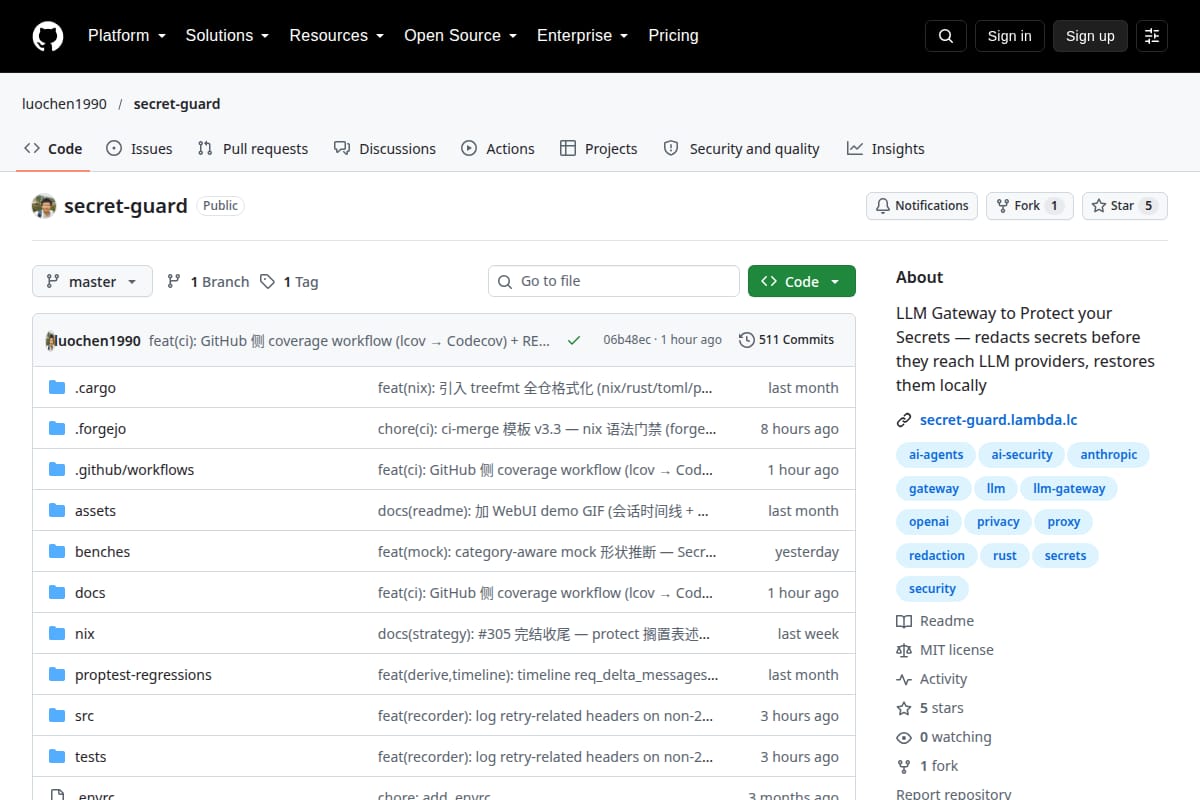
Secret Guard
A local LLM gateway that redacts secrets before requests reach model providers and restores them locally afterward. It is aimed at agent workflows where prompts and tool calls may contain real credentials. |
Developer Tools / Code Assistant | 83 | ↓ -3 | 20 days ago | Details |
#1521
↓ -3
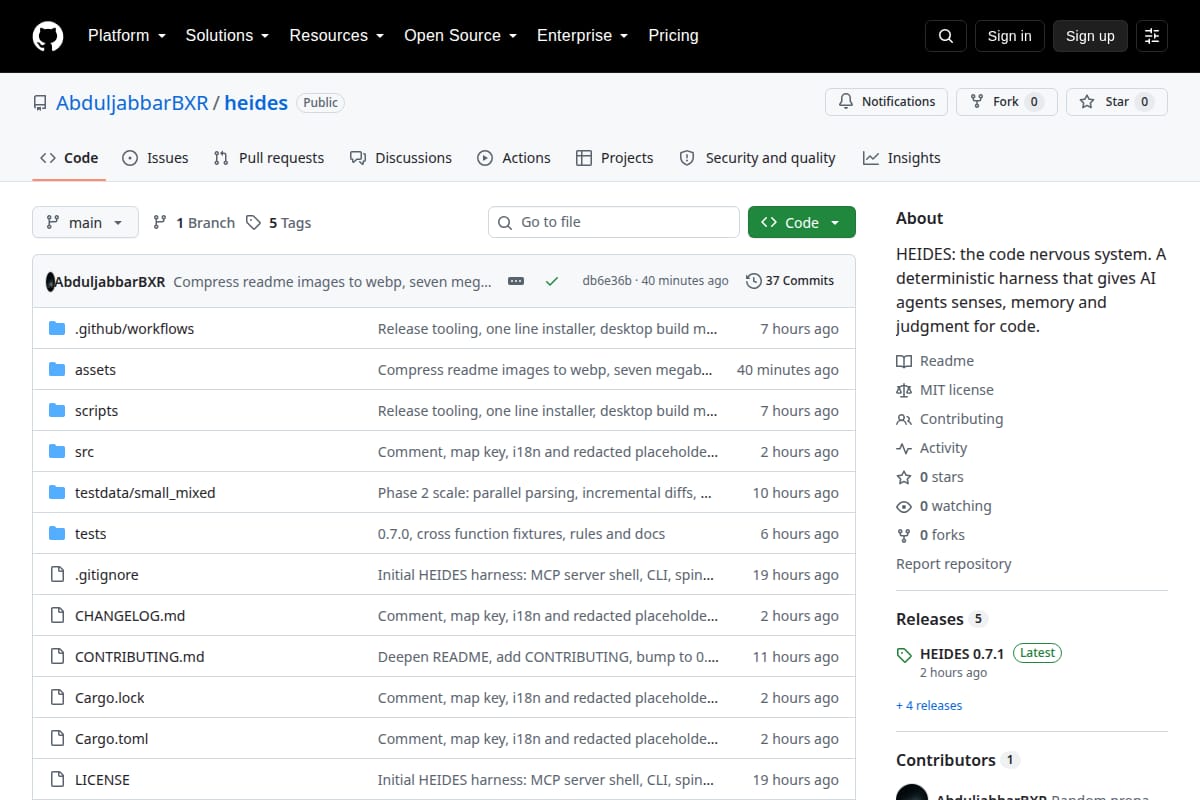
HEIDES
HEIDES is a deterministic local harness for AI coding agents that maps a codebase, grounds plans against the current graph, and checks proposed patches for conflicts, edge cases, and security issues before changes land. |
Developer Tools / Code Assistant | 83 | ↓ -3 | 66 days ago | Details |
#1542
↓ -3
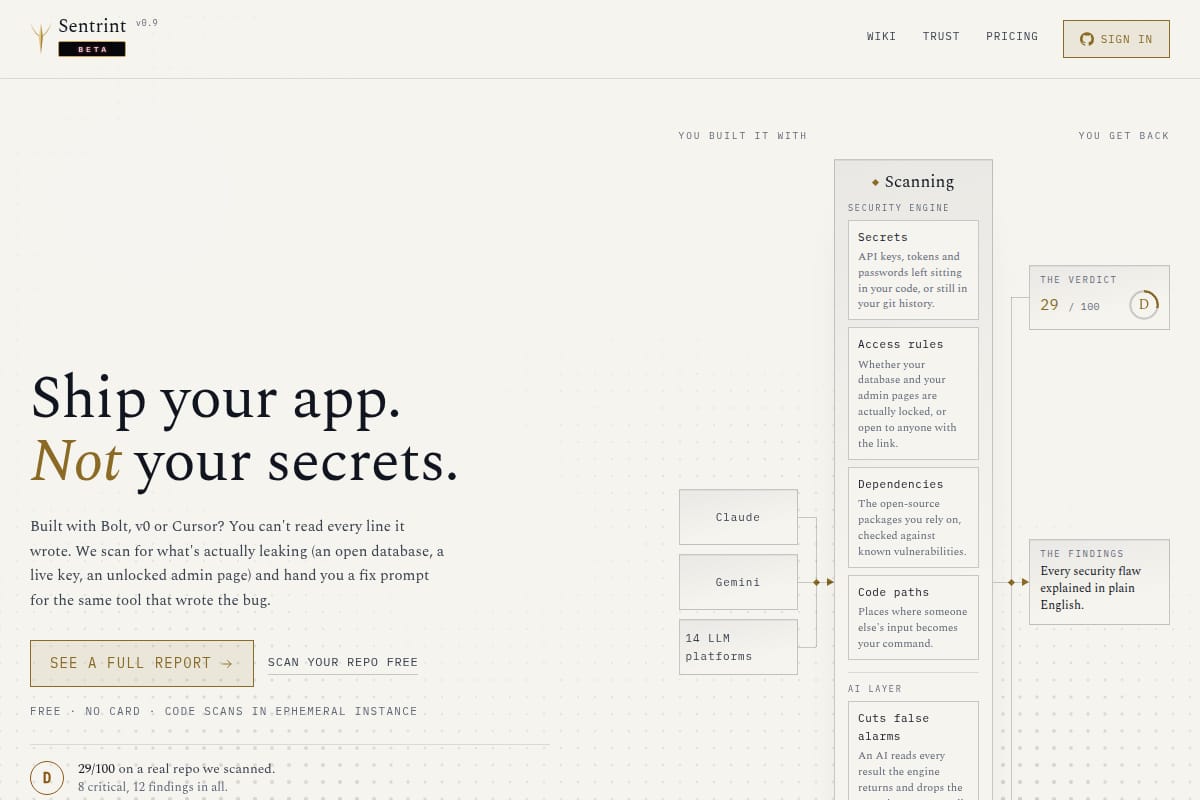
Sentrint
Sentrint is a security scanner for apps built with LLM platforms like Bolt, Cursor, and v0. It scans repos for secrets, access rules, vulnerable dependencies, and risky code paths, then returns plain-English findings and a copy-paste fix prompt. |
Security / Code Security | 83 | ↓ -3 | 79 days ago | Details |
#1544
↓ -3
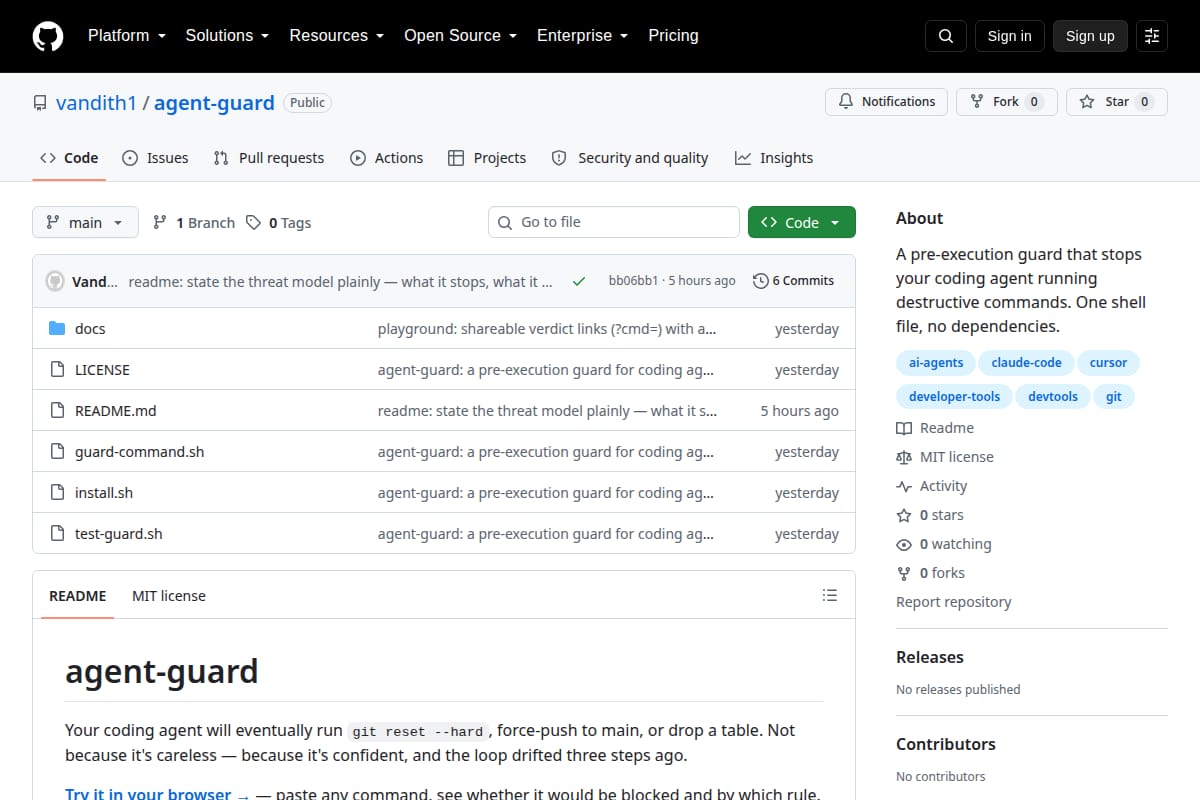
agent-guard
A lightweight shell-based guard that blocks destructive commands before an AI coding agent can run them. It targets risky actions like git reset --hard, rm -rf, force-pushes, and destructive cloud/database commands, with local regex rules and a test script. |
Developer Tools / AI Agent Safety | 83 | ↓ -3 | 83 days ago | Details |
#1556
↓ -3
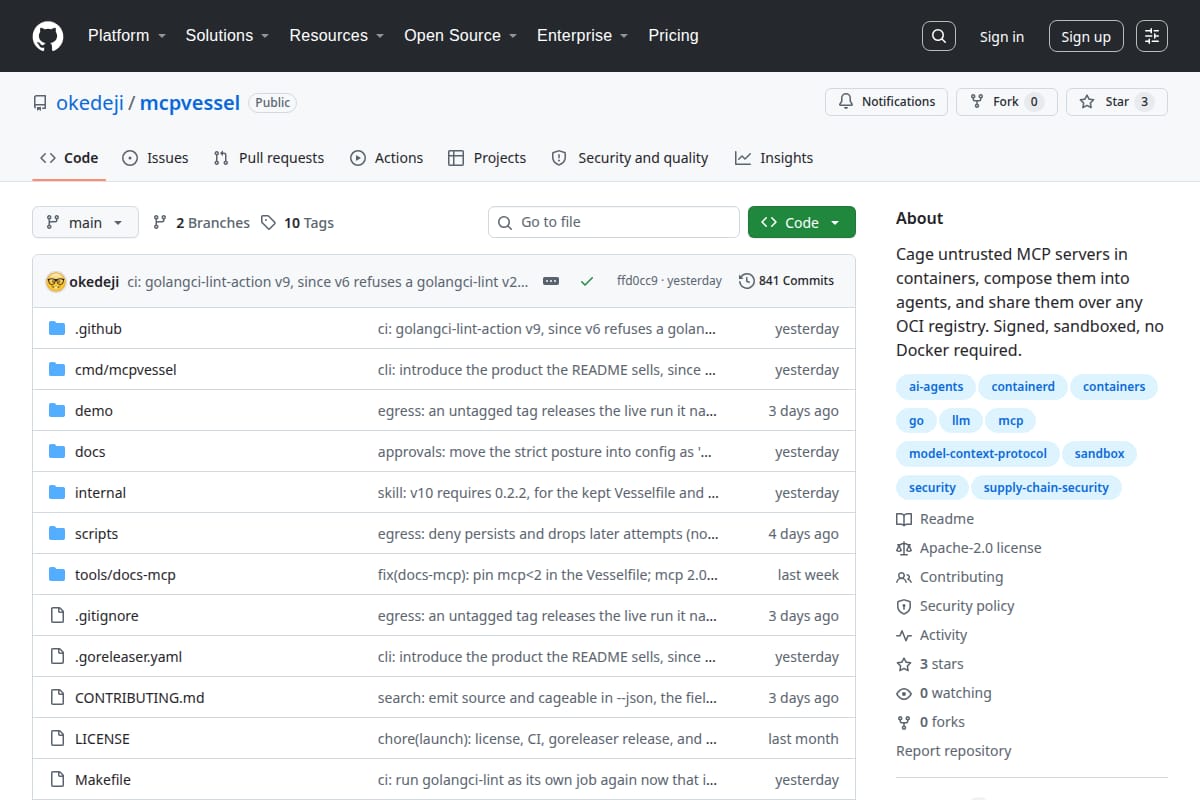
mcpvessel
A CLI for running untrusted MCP servers in sandboxed containers with deny-by-default egress, traffic watching, and host approval workflows. It can also compose servers into agents and expose them over OCI registries. |
Developer Tools / Security / Sandboxing | 83 | ↓ -3 | 94 days ago | Details |
#1582
↓ -3
mcp-audit
A harness that runs MCP servers in a disposable Linux sandbox and logs their real startup behavior, including file access and outbound network connections. |
Developer Tools / AI Tooling | 83 | ↓ -3 | 121 days ago | Details |
#1595
↓ -3
Valmis
An open-source AI agent platform for production workflows, with isolated containers, credential proxying, and support for 100+ business and productivity integrations. |
AI Agents / Workflow Automation | 83 | ↓ -3 | 128 days ago | Details |
#1623
↓ -3
VaultS3
VaultS3 is a self-hosted, S3-compatible object storage server with a built-in dashboard, low RAM usage, and a single-binary deployment. The page highlights features like versioning, WORM, S3 Select, FUSE mount, IAM/OIDC login, search, and event notifications. |
Developer Tools / Storage | 83 | ↓ -3 | 152 days ago | Details |
#1648
↓ -3
Deckard
A Mac-resident MCP server that lets AI agents access Apple services like Mail, Calendar, iCloud Drive, Voice Memos, Reminders, and Contacts over a Tailscale network with per-token ACLs and audit logging. |
Developer Tool / MCP Server | 83 | ↓ -3 | 177 days ago | Details |